


Bad exam habits are easiest to fix before exam day. The PracticeVCE simulation test for the CAS-003 exam reproduces the real atmosphere — timing, pressure, flow — so you can identify what hurts your performance and correct it through repeated, targeted practice.
CompTIA CAS-003 Exam Overview:
| Certification Vendor: | CompTIA |
|---|---|
| Exam Name: | CompTIA Advanced Security Practitioner (CASP+) CAS-003 |
| Exam Number: | CAS-003 |
| Passing Score: | 750 / 900 |
| Exam Price: | $425 USD (may vary by region) |
| Real Exam Qty: | Up to 90 |
| Exam Format: | Multiple choice, Performance-based questions (PBQs) |
| Available Languages: | English, Japanese |
| Certificate Validity Period: | 3 years |
| Exam Duration: | 165 minutes |
| Related Certifications: | CompTIA PenTest+ CompTIA CySA+ CompTIA Security+ |
| Recommended Training: | CompTIA Official CASP+ Training |
| Exam Registration: | CompTIA CASP+ Registration (Pearson VUE) |
| Sample Questions: | DOWNLOAD DEMO |
| Exam Way: | Test center (Pearson VUE) and online proctored exam |
| Pre Condition: | Recommended 10+ years of IT administration experience, including at least 5 years of hands-on technical security experience |
| Official Syllabus URL: | https://www.comptia.org/certifications/casp |
CompTIA CAS-003 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Enterprise Security Architecture | 25% | - Identity and access management design - Cloud and virtualization security architecture - Secure network and system design |
| Topic 2: Technical Integration of Enterprise Security | 36% | - Automation and orchestration of security solutions - Secure deployment and integration of security controls - Cryptography and PKI implementation |
| Topic 3: Risk Management | 19% | - Security compliance and policy enforcement - Business continuity and disaster recovery planning - Enterprise risk frameworks and governance |
| Topic 4: Enterprise Security Operations | 20% | - Monitoring, detection, and incident response - Vulnerability management and threat intelligence |
CAS-003 Exam — Frequently Asked Questions
The CAS-003 exam is a CompTIA certification exam that validates the skills defined in the CompTIA Advanced Security Practitioner (CASP) syllabus above. It forms part of these credential paths: CompTIA Security+, CompTIA CySA+, CompTIA PenTest+. In an economy where certified skills carry growing weight, this credential is one of the clearest ways to demonstrate professional capability in 2026. PracticeVCE prepares you with 683 practice questions in PDF, Desktop Test Engine, and Online Test Engine formats.
CompTIA recommends the following training for the CompTIA Advanced Security Practitioner (CASP) exam:
Follow the training with repeated self-testing — the 683 practice questions from PracticeVCE let you rehearse each topic as often as needed until it holds.
The written refund policy applies: take the CompTIA Advanced Security Practitioner (CASP) exam within 60 days of purchase, and if you do not pass, PracticeVCE refunds you in full. The policy does not apply if the exam is taken within 3 days of purchase, if the exam was never actually taken, or to free materials or expired orders, and the candidate name must match the payer name. Submit a scan of your enrollment slip and the official Score Report PDF within 2 days of the exam; claims are processed within 7 days. You may instead exchange for two free exam products of equal value and keep your original update service. Delivery is by email within 1 minute of purchase — contact support if nothing arrives within 2 hours.
You pass the CompTIA Advanced Security Practitioner (CASP) exam at 750 / 900, and registration costs $425 USD (may vary by region). Since retakes cost the full fee again, repeated simulation runs with the PracticeVCE engines are the economical way to confirm readiness first.
Test center (Pearson VUE) and online proctored exam Register for the CompTIA Advanced Security Practitioner (CASP) exam via these official channels:
Once booked, your PracticeVCE practice questions — delivered within 1 minute of purchase — let preparation begin the same day.
Three versions of the 683 practice questions for the CompTIA Advanced Security Practitioner (CASP) exam: a printable, expert-prepared PDF with instant download; a Desktop Test Engine for Windows whose simulation test reproduces the real exam atmosphere — repeatable as many times as you like, with two practice modes and offline access; and an Online Test Engine for any browser on Windows, Mac, Android, and iOS with test history and performance review. Included as well: a free demo, 365 days of free updates, a 50% renewal discount afterward, unlimited computer installations, and 24/7 online after-sales service.
Recommended 10+ years of IT administration experience, including at least 5 years of hands-on technical security experience Requirements are revised from time to time, so verify the latest on the official CompTIA exam page before scheduling.
The CompTIA Advanced Security Practitioner (CASP) exam consists of Up to 90 within 165 minutes. The PracticeVCE simulation test runs under the same conditions, so you can get accustomed to the atmosphere and work out any pacing habits before they cost you points.
Per the official outline, the CompTIA Advanced Security Practitioner (CASP) exam covers 4 domains, led by Risk Management (19%), Enterprise Security Architecture (25%), and Technical Integration of Enterprise Security (36%). The complete list appears in the topics section above; the 683 practice questions at PracticeVCE span every domain.
CompTIA Advanced Security Practitioner (CASP) Sample Questions:
A company that uses AD is migrating services from LDAP to secure LDAP. During the pilot phase, services are not connecting properly to secure LDAP. Block is an except of output from the troubleshooting session: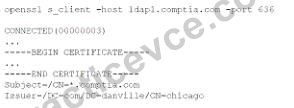
Which of the following BEST explains why secure LDAP is not working? (Select TWO.)
- A. The clients may not trust Chicago by default.
- B. Secure LDAP should be running on UDP rather than TCP.
- C. The company is using the wrong port. It should be using port 389 for secure LDAP.
- D. The clients may not trust idapt by default.
- E. The secure LDAP service is not started, so no connections can be made.
- F. Danvills.com is under a DDoS-inator attack and cannot respond to OCSP requests.
- G. Secure LDAP does not support wildcard certificates.
Correct Answer: C,E 🗳️
A recent overview of the network's security and storage applications reveals a large amount of data that needs to be isolated for security reasons. Below are the critical applications and devices configured on the network:
Firewall
Core switches
RM server
Virtual environment
NAC solution
The security manager also wants data from all critical applications to be aggregated to correlate events from multiple sources. Which of the following must be configured in certain applications to help ensure data aggregation and data isolation are implemented on the critical applications and devices? (Select TWO).
- A. Zones
- B. Data remanants
- C. Port aggregation
- D. NIC teaming
- E. Routing tables
- F. Log forwarding
Correct Answer: A,F 🗳️
An organization implemented a secure boot on its most critical application servers which produce content and capability for other consuming servers A recent incident, however led the organization to implement a centralized attestation service for these critical servers. Which of the following MOST likely explains the nature of the incident that caused the organization to implement this remediation?
- A. An attacker circumvented IEEE 802.1X network-level authentication requirements.
- B. An attacker was able to overwrite an OS integrity measurement register
- C. An attacker leveraged a heap overflow vulnerability in the OS
- D. An attacker masqueraded as an internal DNS server
Correct Answer: B 🗳️
An attacker exploited an unpatched vulnerability in a web framework, and then used an application service account that had an insecure configuration to download a rootkit The attacker was unable to obtain root privileges Instead the attacker then downloaded a crypto-currency mining program and subsequently was discovered The server was taken offline, rebuilt, and patched. Which of the following should the security engineer suggest to help prevent a similar scenario in the future?
- A. Use cron to schedule regular restarts of the service to terminate sessions.
- B. Properly configure SELinux and set it to enforce.
- C. Implement separation of duties.
- D. Remove root privileges from the application service account
- E. Perform regular uncredentialed vulnerability scans
Correct Answer: E 🗳️
The Chief Financial Officer (CFO) of a major hospital system has received a ransom letter that demands a large sum of cryptocurrency be transferred to an anonymous account. If the transfer does not take place within ten hours, the letter states that patient information will be released on the dark web. A partial listing of recent patients is included in the letter. This is the first indication that a breach took place. Which of the following steps should be done FIRST?
- A. Pay the hacker under the condition that all information is destroyed
- B. Notify the appropriate legal authorities and legal counsel
- C. Engage a counter-hacking team to retrieve the data
- D. Review audit logs to determine the extent of the breach
Correct Answer: B 🗳️
Viewing page 1 out of 137 pages.
Viewing questions 1-5 out of 683 questions.
 398 Customer Reviews


