


Plenty of people have earned their certification with steady, honest preparation. PracticeVCE simply makes that steadiness easier to maintain with 371 practice questions and support that does not disappear after checkout.
CompTIA CS0-002日本語 Exam Overview:
| Certification Vendor: | CompTIA |
|---|---|
| Exam Name: | CompTIA CySA+ (CS0-002) Cybersecurity Analyst Certification Exam |
| Exam Number: | CS0-002 |
| Exam Format: | Multiple-choice questions, Performance-based questions |
| Certificate Validity Period: | 3 years |
| Available Languages: | Japanese, Portuguese, English, Thai |
| Exam Price: | USD $392 (may vary by region) |
| Passing Score: | 750 (on a scale of 100–900) |
| Related Certifications: | CompTIA Security+ CompTIA PenTest+ CompTIA Network+ |
| Exam Duration: | 165 minutes |
| Real Exam Qty: | Up to 85 |
| Recommended Training: | CompTIA CySA+ Official Training |
| Exam Registration: | CompTIA Certification Exam Registration |
| Sample Questions: | DOWNLOAD DEMO |
| Exam Way: | Test center or online proctored exam |
| Pre Condition: | Recommended: CompTIA Security+ or equivalent knowledge and 3–4 years of hands-on information security or related experience |
| Official Syllabus URL: | https://www.comptia.org/certifications/cybersecurity-analyst |
CompTIA CS0-002日本語 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Reporting and Communication | 17% | - Security reporting
|
| Topic 2: Vulnerability Management | 30% | - Remediation and mitigation
|
| Topic 3: Incident Response Management | 20% | - Incident handling lifecycle
|
| Topic 4: Security Operations and Monitoring | 33% | - Threat intelligence usage
|
CS0-002日本語 Exam FAQ — Career, Convenience, Current News
PracticeVCE issues a full refund if you take the CompTIA Cybersecurity Analyst (CySA+) Certification Exam (CS0-002日本語版) exam within 60 days of purchase and do not pass. The policy does not apply if the exam is taken within 3 days of purchase, if the exam was never actually taken, or to free materials or expired orders, and the candidate name must match the payer name. Submit a scan of your enrollment slip and the official Score Report PDF within 2 days of the exam; claims are processed within 7 days. Alternatively, exchange for two free exam products of equal value and keep your original update service. Orders arrive by email within 1 minute — contact support if nothing arrives within 2 hours.
The CompTIA Cybersecurity Analyst (CySA+) Certification Exam (CS0-002日本語版) exam contains Up to 85 to complete within 165 minutes. Timed simulation in the PracticeVCE Desktop Test Engine teaches that rhythm before exam day does.
Test center or online proctored exam Register for the CompTIA Cybersecurity Analyst (CySA+) Certification Exam (CS0-002日本語版) exam through these official channels:
After booking, PracticeVCE delivers your practice questions within 1 minute — preparation starts the same day.
The CompTIA Cybersecurity Analyst (CySA+) Certification Exam (CS0-002日本語版) exam requires 750 (on a scale of 100–900) to pass, and registration costs USD $392 (may vary by region). A failed attempt means paying the same fee again — a readiness check with the PracticeVCE engines before booking is the cheaper option.
The CS0-002日本語 exam is a CompTIA certification exam validating the CompTIA Cybersecurity Analyst (CySA+) Certification Exam (CS0-002日本語版) syllabus shown above. It belongs to these credential paths: CompTIA Security+, CompTIA PenTest+, CompTIA Network+. Candidates in 2026 start with PracticeVCE's 371 practice questions, available as a printable PDF, a Windows Desktop Test Engine, and an Online Test Engine — three versions of the same materials.
Recommended: CompTIA Security+ or equivalent knowledge and 3–4 years of hands-on information security or related experience Since requirements change over time, confirm the latest on the official CompTIA exam page before scheduling.
The official CompTIA Cybersecurity Analyst (CySA+) Certification Exam (CS0-002日本語版) outline defines 4 domains. The leading three are Reporting and Communication (17%), Security Operations and Monitoring (33%), and Vulnerability Management (30%). The full list is in the topics section above, and PracticeVCE's 371 practice questions cover each one.
CompTIA recommends these training resources for the CompTIA Cybersecurity Analyst (CySA+) Certification Exam (CS0-002日本語版) exam:
Follow the training with steady self-testing — the 371 practice questions from PracticeVCE help you apply theory and fill any gaps the training leaves.
Three versions of the same study materials: a printable, expert-prepared PDF with free demo download and instant access; a Desktop Test Engine for Windows with customizable simulation and timed modes that works offline; and an Online Test Engine for any browser on Windows, Mac, Android, and iOS with test history and performance review. All 371 practice questions are identical across versions. Every purchase includes 365 days of free updates, a 50% renewal discount afterward, and unlimited computer installations.
CompTIA Cybersecurity Analyst (CySA+) Certification Exam (CS0-002日本語版) Sample Questions:
脅威を傷つけるチームは、ISAC から、攻撃者のプロファイルと活動を追跡する新しい LoC を受け取りました。次のうち、次に更新する必要があるのはどれですか?
- A. ホワイトリスト
- B. ブロックリスト
- C. IDS 署名
- D. DNS
Correct Answer: C 🗳️
Explanation: Only visible for PracticeVCE members. You can sign-up / login (it's free).
次のうち、セキュアブートを有効にできるのはどれですか?
- A. MSM
- B. UEFI
- C. eFuse
- D. PAM
Correct Answer: B 🗳️
Explanation: Only visible for PracticeVCE members. You can sign-up / login (it's free).
組織には、サーバーを 1 つの機能専用にし、不要なサービスを無効にすることを要求するポリシーがあります。Web サーバーの Nmap スキャンからの次の出力があるとします。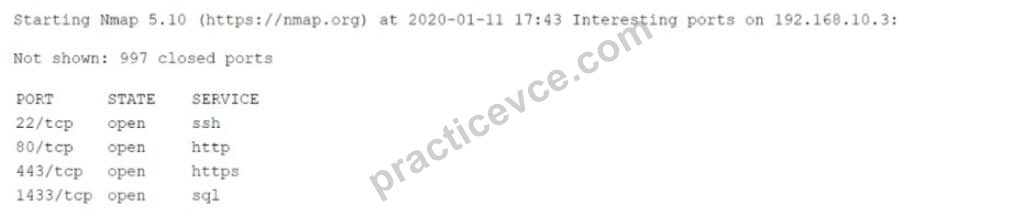
次のどのポートを閉じる必要がありますか?
- A. 22
- B. 1433
- C. 80
- D. 443
Correct Answer: A 🗳️
Explanation: Only visible for PracticeVCE members. You can sign-up / login (it's free).
SIEMソフトウェアでは、セキュリティ分析により、夜間に監視対象ファイルから署名をハッシュするためのいくつかの変更が選択され、その後、ファイルサーバーに対するSMBブルートフォース攻撃が行われました.この動作に基づいて、より深刻な侵害を防ぐために、次のどのアクションを最初に実行する必要があります. ?
- A. ハッシュ署名をチェックし、それらをマルウェア データベースと比較して、ファイルが感染しているかどうかを確認します。
- B. 変更されたすべてのファイルを収集し、以前のベースラインと比較します
- C. 影響を受けるサーバーを、実稼働ネットワークから離れたネットワーク セグメントに物理的に完全に分離します。
- D. 日中のネットワーク トラフィックを収集して、営業時間内にも同じアクティビティが発生しているかどうかを確認します。
Correct Answer: A 🗳️
Explanation: Only visible for PracticeVCE members. You can sign-up / login (it's free).
セキュリティのすべての領域に適切な制御を確保することが、組織が以下を使用する主な理由です。
- A. 取締役および役員。
- B. エンジニアリングの厳密さ。
- C. インシデント対応計画。
- D. フレームワーク。
Correct Answer: D 🗳️
Explanation: Only visible for PracticeVCE members. You can sign-up / login (it's free).
Viewing page 1 out of 75 pages.
Viewing questions 1-5 out of 371 questions.
 0 Customer Reviews
