

CIPT Exam Brain Dumps - Study Notes and Theory [May-2023]
100% Guaranteed Results CIPT Unlimited 216 Questions
The IAPP CIPT (Certified Information Privacy Technologist) Exam is a certification exam offered by the International Association of Privacy Professionals (IAPP). This exam is designed to assess an individual's understanding of privacy laws, regulations, and practices related to information technology. The certification is designed for professionals who work in the field of information technology and are responsible for ensuring the privacy of personal information.
Study Courses for This Exam
If candidates need to revise for the actual validation, they should invest in relevant training courses. IAPP recommends at least 30 hours of study for those preparing for the official CIPT test. The Advanced Privacy Knowledge to Improve Your Technology Development Skills training prepares the candidates for advanced knowledge of data privacy and furnishes them with technology skills. The course also helps the candidate to identify cybersecurity threats and privacy to data and delves into software as well as development lifecycles. In addition, this class equips the specialists with strategies to implement data privacy and mitigating cyber threats. Particularly, such training is appropriate for data privacy specialists such as software developers, professionals in the information security industry, data solutions architects, network engineers as well as privacy engineers. As you might assume, the course prepares the candidates for the CIPT designation and its curriculum comprises privacy-by-design concepts, executing data- as well as process-oriented techniques in support of data privacy policies. It also covers handling threats from artificial intelligence and tracking locations, among others. In a nutshell, here are the given domains discussed in the course:
- Handling privacy-related technological challenges.
- Privacy engineering;
- The important role of a technology specialist in privacy;
- Neutralizing threats and improving privacy;
- Basic concepts in technology;
You can get this course as a separate unit or can opt for the cost-effective training option, which includes ‘Privacy in Technology’ online class, one year’s IAPP membership, sample questions, the exam voucher, and two textbooks that are digital.
Achieving CIPT certification can have a significant impact on an individual's career prospects. It demonstrates to employers and clients that they have the knowledge and skills needed to manage privacy and data protection in a technology-driven world. In addition, CIPT certification is recognized worldwide and is highly regarded within the privacy profession. As such, it can open up new opportunities for career advancement and professional growth.
NEW QUESTION # 32
SCENARIO
It should be the most secure location housing data in all of Europe, if not the world. The Global Finance Data Collective (GFDC) stores financial information and other types of client data from large banks, insurance companies, multinational corporations and governmental agencies. After a long climb on a mountain road that leads only to the facility, you arrive at the security booth. Your credentials are checked and checked again by the guard to visually verify that you are the person pictured on your passport and national identification card.
You are led down a long corridor with server rooms on each side, secured by combination locks built into the doors. You climb a flight of stairs and are led into an office that is lighted brilliantly by skylights where the GFDC Director of Security, Dr. Monique Batch, greets you. On the far wall you notice a bank of video screens showing different rooms in the facility. At the far end, several screens show different sections of the road up the mountain Dr. Batch explains once again your mission. As a data security auditor and consultant, it is a dream assignment: The GFDC does not want simply adequate controls, but the best and most effective security that current technologies allow.
"We were hacked twice last year," Dr. Batch says, "and although only a small number of records were stolen, the bad press impacted our business. Our clients count on us to provide security that is nothing short of impenetrable and to do so quietly. We hope to never make the news again." She notes that it is also essential that the facility is in compliance with all relevant security regulations and standards.
You have been asked to verify compliance as well as to evaluate all current security controls and security measures, including data encryption methods, authentication controls and the safest methods for transferring data into and out of the facility. As you prepare to begin your analysis, you find yourself considering an intriguing question: Can these people be sure that I am who I say I am?
You are shown to the office made available to you and are provided with system login information, including the name of the wireless network and a wireless key. Still pondering, you attempt to pull up the facility's wireless network, but no networks appear in the wireless list. When you search for the wireless network by name, however it is readily found.
Why would you recommend that GFC use record encryption rather than disk, file or table encryption?
- A. Record encryption allows for encryption of personal data only.
- B. Record encryption is asymmetric, a stronger control measure.
- C. Record encryption is granular, limiting the damage of potential breaches.
- D. Record encryption involves tag masking, so its metadata cannot be decrypted
Answer: C
NEW QUESTION # 33
What is the most effective first step to take to operationalize Privacy by Design principles in new product development and projects?
- A. Set up an online Privacy Impact Assessment tool to facilitate Privacy by Design compliance.
- B. Implementing a mandatory privacy review and legal approval process.
- C. Conduct annual Privacy by Design training and refreshers for all impacted personnel.
- D. Obtain leadership buy-in for a mandatory privacy review and approval process.
Answer: D
Explanation:
This is the most effective first step to operationalize Privacy by Design principles in new product development and projects. It is important to obtain leadership buy-in for a mandatory privacy review and approval process to ensure that privacy is a priority throughout the organization.
NEW QUESTION # 34
SCENARIO
Wesley Energy has finally made its move, acquiring the venerable oil and gas exploration firm Lancelot from its long-time owner David Wilson. As a member of the transition team, you have come to realize that Wilson's quirky nature affected even Lancelot's data practices, which are maddeningly inconsistent. "The old man hired and fired IT people like he was changing his necktie," one of Wilson's seasoned lieutenants tells you, as you identify the traces of initiatives left half complete.
For instance, while some proprietary data and personal information on clients and employees is encrypted, other sensitive information, including health information from surveillance testing of employees for toxic exposures, remains unencrypted, particularly when included within longer records with less-sensitive data.
You also find that data is scattered across applications, servers and facilities in a manner that at first glance seems almost random.
Among your preliminary findings of the condition of data at Lancelot are the following:
* Cloud technology is supplied by vendors around the world, including firms that you have not heard of.
You are told by a former Lancelot employee that these vendors operate with divergent security requirements and protocols.
* The company's proprietary recovery process for shale oil is stored on servers among a variety of less-sensitive information that can be accessed not only by scientists, but by personnel of all types at most company locations.
* DES is the strongest encryption algorithm currently used for any file.
* Several company facilities lack physical security controls, beyond visitor check-in, which familiar vendors often bypass.
* Fixing all of this will take work, but first you need to grasp the scope of the mess and formulate a plan of action to address it.
Which is true regarding the type of encryption Lancelot uses?
- A. Its decryption key is derived from its encryption key.
- B. It employs the data scrambling technique known as obfuscation.
- C. It uses a single key for encryption and decryption.
- D. It is a data masking methodology.
Answer: B
NEW QUESTION # 35
What is the goal of privacy enhancing technologies (PETS) like multiparty computation and differential privacy?
- A. To facilitate audits of third party vendors.
- B. To protect sensitive data while maintaining its utility.
- C. To standardize privacy activities across organizational groups.
- D. To protect the security perimeter and the data items themselves.
Answer: B
NEW QUESTION # 36
A BaaS provider backs up the corporate data and stores it in an outsider provider under contract with the organization. A researcher notifies the organization that he found unsecured data in the cloud. The organization looked into the issue and realized $ne of its backups was misconfigured on the outside provider's cloud and the data fully exposed to the open internet. They quickly secured the backup. Which is the best next step the organization should take?
- A. Review its contract with the outside provider.
- B. Investigate how the researcher discovered the unsecured data.
- C. Investigate using alternate BaaS providers or on-premise backup systems.
- D. Review the content of the data exposed.
Answer: A
Explanation:
The best next step the organization should take is to review its contract with the outside provider. This will help the organization to identify the responsibilities of the outside provider and the organization in the event of a data breach.
NEW QUESTION # 37
Which of the following statements is true regarding software notifications and agreements?
- A. It is a good practice to provide users with information about privacy prior to software installation.
- B. "Just in time" software agreement notifications provide users with a final opportunity to modify the agreement.
- C. Website visitors must view the site's privacy statement before downloading software.
- D. Software agreements are designed to be brief, while notifications provide more details.
Answer: A
NEW QUESTION # 38
What is the main function of the Amnesic Incognito Live System or TAILS device?
- A. It allows the user to run a self-contained computer from a USB device.
- B. It causes a system to suspend its security protocols.
- C. It accesses systems with a credential that leaves no discernable tracks.
- D. It encrypts data stored on any computer on a network.
Answer: A
Explanation:
Explanation/Reference: https://www.wired.co.uk/article/tails-operating-software
NEW QUESTION # 39
What would be an example of an organization transferring the risks associated with a data breach?
- A. Using a third-party service to process credit card transactions.
- B. Purchasing insurance to cover the organization in case of a breach.
- C. Applying industry standard data handling practices to the organization' practices.
- D. Encrypting sensitive personal data during collection and storage
Answer: B
Explanation:
Explanation/Reference: http://www.hpso.com/Documents/pdfs/newsletters/firm09-rehabv1.pdf
NEW QUESTION # 40
When writing security policies, the most important consideration is to?
- A. Follow industry best practices.
- B. Ensure they cover enough details for common situations.
- C. Ensure they are based on the organization's risk profile.
- D. Require all employees to read and acknowledge their understanding.
Answer: C
Explanation:
the most important consideration when writing security policies is to ensure they are based on the organization's risk profile. This means that the policies should be tailored to address the specific risks faced by the organization.
NEW QUESTION # 41
SCENARIO
Wesley Energy has finally made its move, acquiring the venerable oil and gas exploration firm Lancelot from its long-time owner David Wilson. As a member of the transition team, you have come to realize that Wilson's quirky nature affected even Lancelot's data practices, which are maddeningly inconsistent. "The old man hired and fired IT people like he was changing his necktie," one of Wilson's seasoned lieutenants tells you, as you identify the traces of initiatives left half complete.
For instance, while some proprietary data and personal information on clients and employees is encrypted, other sensitive information, including health information from surveillance testing of employees for toxic exposures, remains unencrypted, particularly when included within longer records with less-sensitive data. You also find that data is scattered across applications, servers and facilities in a manner that at first glance seems almost random.
Among your preliminary findings of the condition of data at Lancelot are the following:
* Cloud technology is supplied by vendors around the world, including firms that you have not heard of. You are told by a former Lancelot employee that these vendors operate with divergent security requirements and protocols.
* The company's proprietary recovery process for shale oil is stored on servers among a variety of less- sensitive information that can be accessed not only by scientists, but by personnel of all types at most company locations.
* DES is the strongest encryption algorithm currently used for any file.
* Several company facilities lack physical security controls, beyond visitor check-in, which familiar vendors often bypass.
* Fixing all of this will take work, but first you need to grasp the scope of the mess and formulate a plan of action to address it.
Which is true regarding the type of encryption Lancelot uses?
- A. Its decryption key is derived from its encryption key.
- B. It employs the data scrambling technique known as obfuscation.
- C. It uses a single key for encryption and decryption.
- D. It is a data masking methodology.
Answer: B
Explanation:
Explanation/Reference: https://www.techopedia.com/definition/25015/data-obfuscation-do
NEW QUESTION # 42
SCENARIO - Please use the following to answer the next question:
Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephor, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q:s business.
model, resources are contracted as needed instead of permanently employed.
The table below indicates some of the personal information Clean-Q requires as part of its business operations: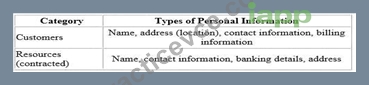
Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation.
Therefore, the Clean-Q permanent employee base is not included as part of this scenario.
With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q:s traditional supply and demand system that has caused some overlapping bookings.
In a business statrategy session held by senior management recently, Clearning invited vendors to present potential solutions to their current operational issues. These vendors includes included Application development and Cloud solution providers, presenting their proposed solution and platforms.
The Managing Direct opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform. A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information.
A customer facing web interface that enables customers to register, manage and submit cleaning service requests online.
A resource facing web interface that enables resources to apply and manage their assigned jobs.
An online payment facility for customer to pay for services.
What is a key consideration for assessing external service providers like LeadOps, which will conduct personal information processing operations on Clean-Q:s behalf?
- A. Establishing a relationship with the Managing Director of LeadOps.
- B. Understanding LeadOps costing model.
- C. Recognizing the value of LeadOps website holding a verified security certificate.
- D. Obtaining knowledge of LeadOps information handling practices and information security environment.
Answer: A
NEW QUESTION # 43
What is a mistake organizations make when establishing privacy settings during the development of applications?
- A. Providing a user with too much third-party information.
- B. Failing to use "Do Not Track" technology
- C. Failing to get explicit consent from a user on the use of cookies.
- D. Providing a user with too many choices.
Answer: D
NEW QUESTION # 44
SCENARIO
Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephone, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q's business model, resources are contracted as needed instead of permanently employed.
The table below indicates some of the personal information Clean-Q requires as part of its business operations:
Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation. Therefore, the Clean-Q permanent employee base is not included as part of this scenario.
With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q's traditional supply and demand system that has caused some overlapping bookings.
Ina business strategy session held by senior management recently, Clear-Q invited vendors to present potential solutions to their current operational issues. These vendors included Application developers and Cloud-Q's solution providers, presenting their proposed solutions and platforms.
The Managing Director opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform: A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information.
* A customer facing web interface that enables customers to register, manage and submit cleaning service requests online.
* A resource facing web interface that enables resources to apply and manage their assigned jobs.
* An online payment facility for customers to pay for services.
Which question would you most likely ask to gain more insight about LeadOps and provide practical privacy recommendations?
- A. Where are LeadOps' operations and hosting services located?
- B. Does LeadOps practice agile development and maintenance of their system?
- C. What is LeadOps' annual turnover?
- D. How big is LeadOps' employee base?
Answer: B
NEW QUESTION # 45
Which activity would best support the principle of data quality?
- A. Providing notice to the data subject regarding any change in the purpose for collecting such data.
- B. Delivering information in a format that the data subject understands.
- C. Ensuring that information remains accurate.
- D. Ensuring that the number of teams processing personal information is limited.
Answer: D
NEW QUESTION # 46
What is the main benefit of using a private cloud?
- A. The ability to restrict data access to employees and contractors.
- B. The ability to outsource data support to a third party.
- C. The ability to cut costs for storing, maintaining, and accessing data.
- D. The ability to use a backup system for personal files.
Answer: A
Explanation:
Explanation/Reference:
NEW QUESTION # 47
SCENARIO
Looking back at your first two years as the Director of Personal Information Protection and Compliance for the Berry Country Regional Medical Center in Thorn Bay, Ontario, Canada, you see a parade of accomplishments, from developing state-of-the-art simulation based training for employees on privacy protection to establishing an interactive medical records system that is accessible by patients as well as by the medical personnel. Now, however, a question you have put off looms large: how do we manage all the data-not only records produced recently, but those still on hand from years ago? A data flow diagram generated last year shows multiple servers, databases, and work stations, many of which hold files that have not yet been incorporated into the new records system. While most of this data is encrypted, its persistence may pose security and compliance concerns. The situation is further complicated by several long-term studies being conducted by the medical staff using patient information. Having recently reviewed the major Canadian privacy regulations, you want to make certain that the medical center is observing them.
You also recall a recent visit to the Records Storage Section, often termed "The Dungeon" in the basement of the old hospital next to the modern facility, where you noticed a multitude of paper records. Some of these were in crates marked by years, medical condition or alphabetically by patient name, while others were in undifferentiated bundles on shelves and on the floor. The back shelves of the section housed data tapes and old hard drives that were often unlabeled but appeared to be years old. On your way out of the dungeon, you noticed just ahead of you a small man in a lab coat who you did not recognize. He carried a batch of folders under his arm, apparently records he had removed from storage.
Which cryptographic standard would be most appropriate for protecting patient credit card information in the records system?
- A. Symmetric Encryption
- B. Obfuscation
- C. Asymmetric Encryption
- D. Hashing
Answer: A
Explanation:
To protect patient credit card information in the records system at Berry Country Regional Medical Center, an appropriate cryptographic standard to use would be option B: Symmetric Encryption.
Symmetric encryption uses a single secret key to encrypt and decrypt data. It is a fast and efficient method of encryption that can provide strong protection for sensitive data such as credit card information when implemented correctly.
NEW QUESTION # 48
SCENARIO - Please use the following to answer the next question:
Wesley Energy has finally made its move, acquiring the venerable oil and gas exploration firm Lancelot from its long-time owner David Wilson. As a member of the transition team, you have come to realize that Wilson s quirky nature affected even Lancelot s data practices, which are maddeningly inconsistent. "The old man hired and fired IT people like he was changing his necktie,'1 one of Wilson s seasoned lieutenants tells you, as you identify the traces of initiatives left half complete.
For instance, while some proprietary data and personal information on clients and employees is encrypted, other sensitive^ information, including health information from surveillance testing of employees for toxic exposures, remains unencrypted, particularly when included within longer records with less-sensitive data.
You also find that data is scattered across applications, servers and facilities in a manner that at first glance seems almost random.
Among your preliminary findings of the condition of data at Lancelot are the following:
Cloud technology is supplied by vendors around the world, including firms that you have not heard of. You are told by a former Lancelot employee that these vendors operate with divergent security requirements and protocols.
o The company s proprietary recovery process for shale oil is stored on servers among a variety of less-sensitive information that can be accessed not only by scientists, but by personnel of all types at most company locations.
o DES is the strongest encryption algorithm currently used for any file.
o Several company facilities lack physical security controls beyond visitor check-in, which familiar vendors often bypass.
o Fixing all of this will take work, but first you need to grasp the scope of the mess and formulate a plan of action to address it.
Which is true regarding the type of encryption Lancelot uses?
- A. It employs the data scrambling technique known as obfuscation.
- B. It uses a single key for encryption and decryption.
- C. It is a data masking methodology.
- D. Its decryption key is derived from its encryption key.
Answer: D
NEW QUESTION # 49
Which Organisation for Economic Co-operation and Development (OECD) privacy protection principle encourages an organization to obtain an individual s consent before transferring personal information?
- A. Individual participation.
- B. Accountability.
- C. Purpose specification.
- D. Collection limitation.
Answer: B
NEW QUESTION # 50
A developer is designing a new system that allows an organization's helpdesk to remotely connect into the device of the individual to provide support Which of the following will be a privacy technologist's primary concern"?
- A. Geolocation
- B. Geofencing
- C. Geo-tagging
- D. Geo-tracking
Answer: A
Explanation:
a privacy technologist's primary concern when designing a new system that allows an organization's helpdesk to remotely connect into the device of the individual to provide support would be geolocation.
NEW QUESTION # 51
SCENARIO - Please use the following to answer the next question:
Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephor, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q:s business.
model, resources are contracted as needed instead of permanently employed.
The table below indicates some of the personal information Clean-Q requires as part of its business operations:
Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation.
Therefore, the Clean-Q permanent employee base is not included as part of this scenario.
With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q:s traditional supply and demand system that has caused some overlapping bookings.
In a business statrategy session held by senior management recently, Clearning invited vendors to present potential solutions to their current operational issues. These vendors includes included Application development and Cloud solution providers, presenting their proposed solution and platforms.
The Managing Direct opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform. A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information.
A customer facing web interface that enables customers to register, manage and submit cleaning service requests online.
A resource facing web interface that enables resources to apply and manage their assigned jobs.
An online payment facility for customer to pay for services.
Considering that LeadOps will host/process personal information on behalf of Clean-Q remotely, what is an appropriate next step for Clean-Q senior management to assess LeadOps' appropriateness?
- A. Nothing at this stage as the Managing Director has made a decision.
- B. Obtain a legal opinion from an external law firm on contracts management.
- C. Involve the Information Security team to understand in more detail the types of services and solutions LeadOps is proposing.
- D. Determine if any Clean-Q competitors currently use LeadOps as a solution.
Answer: B
NEW QUESTION # 52
SCENARIO - Please use the following to answer the next question:
WebTracker Limited is a cloud-based online marketing service located in London. Last year, WebTracker migrated its IT infrastructure to the cloud provider AmaZure, which provides SQL Databases and Artificial Intelligence services to WebTracker. The roles and responsibilities between the two companies have been formalized in a standard contract, which includes allocating the role of data controller to WebTracker.
The CEO of WebTracker, Mr. Bond, would like to assess the effectiveness of AmaZure s privacy controls, and he recently decided to hire you as an independent auditor. The scope of the engagement is limited only to the marketing service! Provided by WebTracker, you will not be evaluating any internal data processing activity, such as HR or Payroll.
This ad-hoc audit was triggered due to a future partnership between WebTracker and SmartHome-a partnership that will not require any data sharing. SmartHome is based in the USA, and most recently has dedicated substantial resources to developing smart refrigerators that can suggest the recommended daily calorie intake based on DNA information. This and other personal data is collected by WebTracker.
To get an idea of the scope of work involved, you have decided to start reviewing the company s documentation and interviewing key staff to understand potential privacy risks. The results of this initial work include the following notes:
To get an idea of the scope of work involved, you have decided to start reviewing the company s documentation and interviewing key staff to understand potential privacy risks. The results of this initial work include the following notes:
o There are several typos in the current privacy notice of WebTracker. and you were not able to find the privacy notice for SmartHome.
o You were unable to identify all the sub-processors working for SmartHome. No subcontractor is indicated in the cloud agreement with AmaZure. which is responsible for the support and maintenance of the cloud infrastructure.
o There are data flows representing personal data being collected from the internal employees of WebTracker, including an interface from the HR system.
o Part of the DNA data collected by WebTracker was from employees, as this was a prototype approved by the CEO of WebTracker.
o All the WebTracker and SmartHome customers are based in USA and Canada Which of the following issues is most likely to require an investigation by the Chief Privacy Officer (CPO) of WebTracker?
- A. AmaZure sends newsletter to WebTracker customers, as approved by the Marketing Manager
- B. File Integrity Monitoring is being deployed in SQL servers, as indicated by the IT Architect Manager.
- C. Data flows use encryption for data at rest, as defined by the IT manager.
- D. Employees personal data are being stored in a cloud HR system, as approved by the HR Manager.
Answer: A
NEW QUESTION # 53
......
CIPT Dumps PDF - Want To Pass CIPT Fast: https://www.practicevce.com/IAPP/CIPT-practice-exam-dumps.html
CIPT Practice Exam Dumps Exam: https://drive.google.com/open?id=1ZxmC2RZiv9QjciYJIcHeaTs1dXie0lu5