

PDF (New 2024) Actual Microsoft MS-100 Exam Questions
Dumps Moneyack Guarantee - MS-100 Dumps UpTo 90% Off
NEW QUESTION # 143
You have several devices enrolled in Microsoft Intune.
You have a Microsoft Azure Active Directory (Azure AD) tenant that includes the users shown in the following table.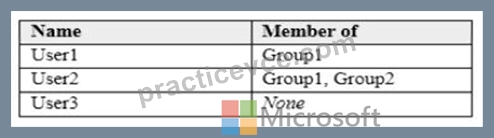
The device type restrictions in Intune are configured as shown in the following table.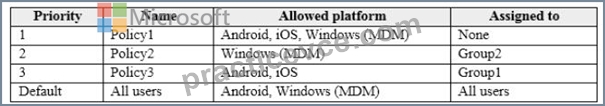
You add User3 as a device enrollment manager in Intune.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.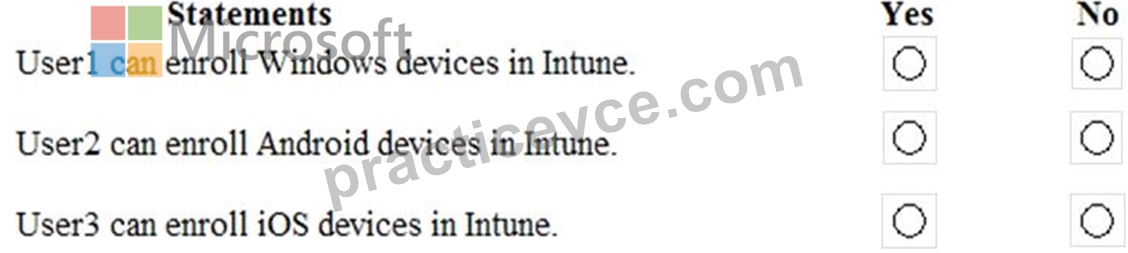
Answer:
Explanation: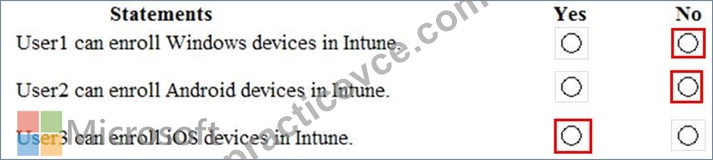
Reference:
https://docs.microsoft.com/en-us/intune/enrollment/enrollment-restrictions-set
NEW QUESTION # 144
You have an on-premises Microsoft Exchange Server organization that contains 500 mailboxes and a third-party email archive solution.
You have a Microsoft 365 tenant that contains a user named User1.
You plan to use the User1 account to perform a PST import of the archive mailboxes to the tenant.
Which two roles does User1 require to perform the import? The solution must use the principle of least privilege. Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Records Management
- B. Exchange admin
- C. eDiscovery Manager
- D. Mail Recipients
- E. Mailbox Import Export
Answer: D,E
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/importing-pst-files-to-office-365?view=o365-worldw
NEW QUESTION # 145
You have a Microsoft 365 subscription.
You are configuring permissions for Security & Compliance.
You need to ensure that the users can perform the tasks shown in the following table.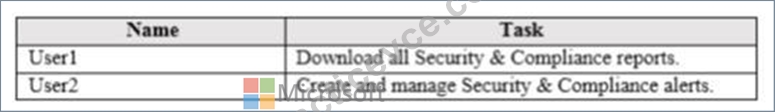
The solution must use the principle of least privilege.
To which role should you assign each user? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.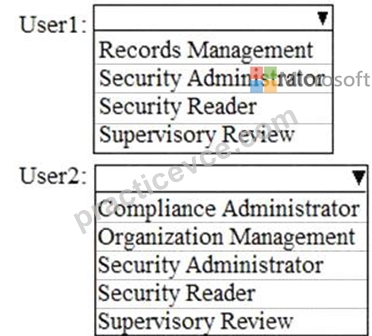
Answer:
Explanation: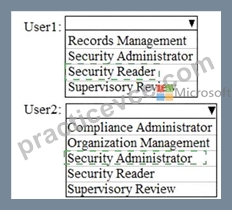
Explanation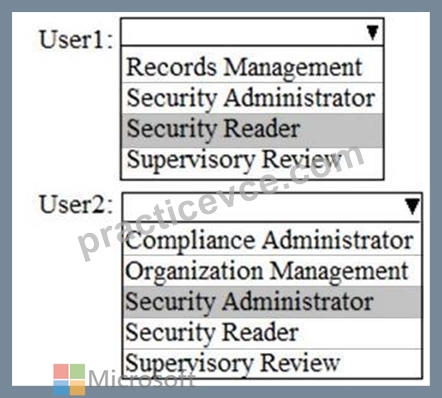
Security Reader: Members can manage security alerts (view only), and also view reports and settings of security features.
Security Administrator, Compliance Administrator and Organization Management can manage alerts.
However, Security Administrator has the least privilege.
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/permissions-in-the-security-and-compliance-cent
NEW QUESTION # 146
You have a Microsoft 365 subscription.
You view the service advisories shown in the following exhibit.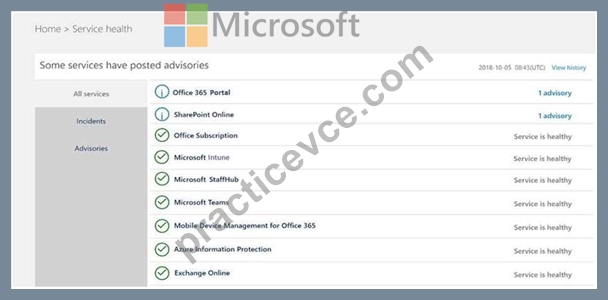
You need to ensure that users who administer Microsoft SharePoint Online can view the advisories to investigate service health issues.
Which role should you assign to the users?
- A. Message Center reader
- B. Reports reader
- C. Compliance administrator
- D. Service administrator
Answer: D
Explanation:
People who are assigned the global admin or service administrator role can view service health. To allow Exchange, SharePoint, and Skype for Business admins to view service health, they must also be assigned the Service admin role. For more information about roles that can view service health.
Reference:
https://docs.microsoft.com/en-us/office365/enterprise/view-service-health
NEW QUESTION # 147
You network contains an on-premises Active Directory domain named contoso.com. The domain contains a Microsoft Exchange Server 2019 organization.
You plan to sync the domain to Azure Active Directory (Azure AD) and to enable device writeback and group writeback.
You need to identify which group types will sync from Azure AD.
Which two group types should you identify? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
NOTE: Each correct selection is worth one point.
- A. An Office 365 group that uses the Dynamic User membership type
- B. An Office 365 group that uses the assigned membership type
- C. A security groups that uses the Dynamic Device membership type.
- D. A security group that uses the Dynamic User membership type
- E. A security group uses the Assigned membership type
Answer: A,B
Explanation:
Explanation
Group writeback in Azure AD Connect synchronizes Office 365 groups only from Azure Active Directory back to the on-premise Active Directory.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-preview
NEW QUESTION # 148
You need to meet the security requirements for User3. The solution must meet the technical requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.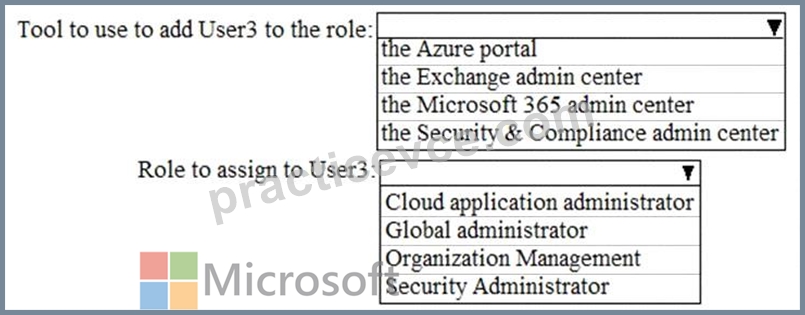
Answer:
Explanation: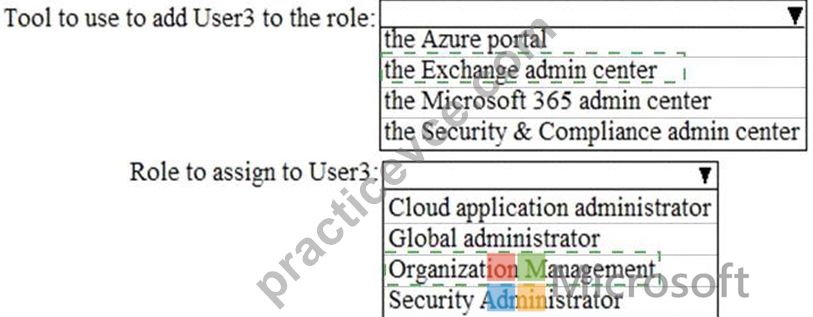
Explanation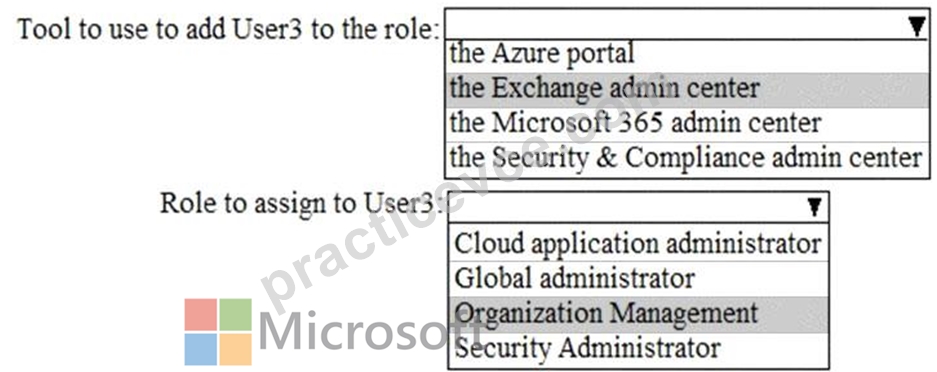
References:
https://docs.microsoft.com/en-us/office365/SecurityCompliance/eop/feature-permissions-in-eop
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answer and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. When you are ready to answer a question, click the Overview Contoso, Ltd. is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
The offices have the users and devices shown in the following table.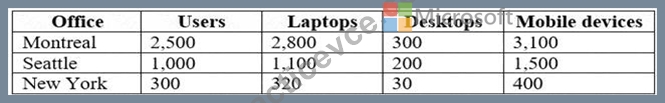
Contoso recently purchased a Microsoft 365 E5 subscription.
Existing Environment
The network contains an Active directory forest named contoso.com and a Microsoft Azure Active Directory (Azure AD) tenant named contoso.onmicrosoft.com.
You recently configured the forest to sync to the Azure AD tenant.
You add and then verify adatum.com as an additional domain name.
All servers run Windows Server 2016.
All desktop computers and laptops run Windows 10 Enterprise and are joined to contoso.com.
All the mobile devices in the Montreal and Seattle offices run Android. All the mobile devices in the New York office run iOS.
Contoso has the users shown in the following table.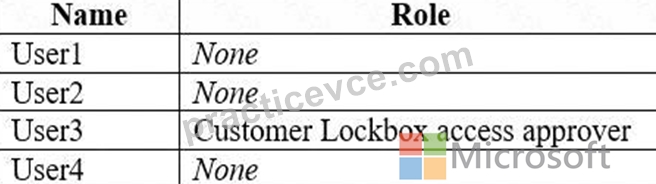
Contoso has the groups shown in the following table.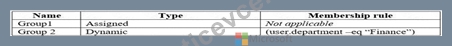
Microsoft Office 365 licenses are assigned only to Group2.
The network also contains external users from a vendor company who have Microsoft accounts that use a suffix of @outlook.com.
Requirements
Planned Changes
Contoso plans to provide email addresses for all the users in the following domains:
* East.adatum.com
* Contoso.adatum.com
* Humongousinsurance.com
Technical Requirements
Contoso identifies the following technical requirements:
* All new users must be assigned Office 365 licenses automatically.
* The principle of least privilege must be used whenever possible.
Security Requirements
Contoso identifies the following security requirements:
* Vendors must be able to authenticate by using their Microsoft account when accessing Contoso resources.
* User2 must be able to view reports and schedule the email delivery of security and compliance reports.
* The members of Group1 must be required to answer a security question before changing their password.
* User3 must be able to manage Office 365 connectors.
* User4 must be able to reset User3 password.
NEW QUESTION # 149
You have a Microsoft Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.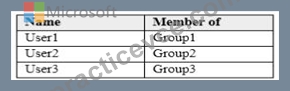
Your company uses Windows Defender Advanced Threat Protection (ATP). Windows Defender ATP contains the roles shown in the following table.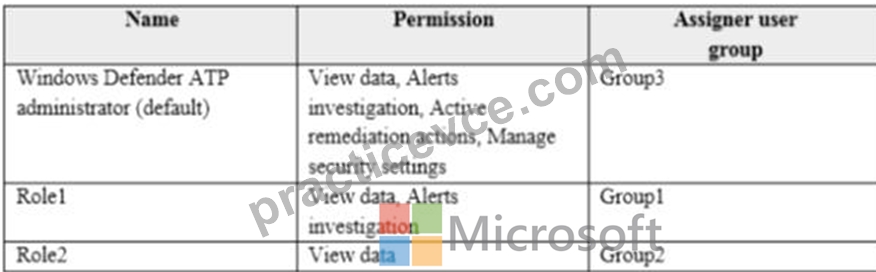
Windows Defender ATP contains the device groups shown in the following table.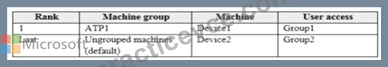
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.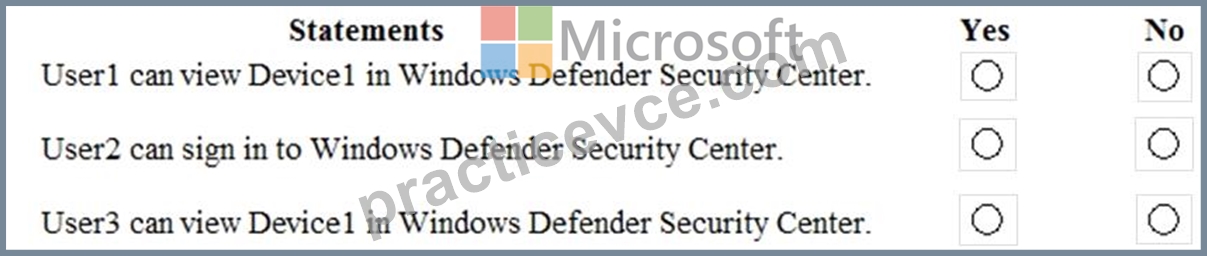
Answer:
Explanation: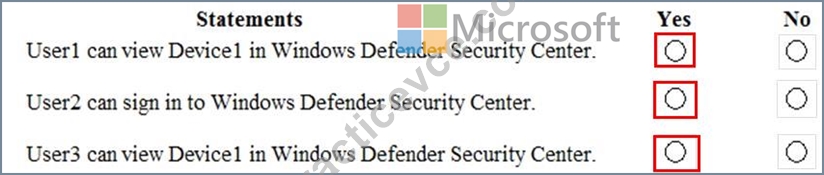
Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/user-roles
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/rbac
NEW QUESTION # 150
Your network contains an on-premises Active Directory domain. The domain contains a server named Server1. Server1 has a share named Share1 that contains the files shown in the following table.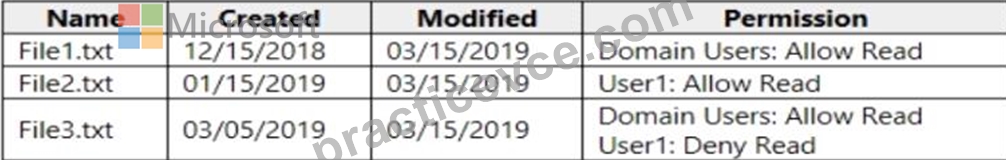
You have a hybrid deployment of Microsoft 365.
You create a Microsoft SharePoint site collection named Col lection1.
You plan to migrate Share1 to a document library in Collection1
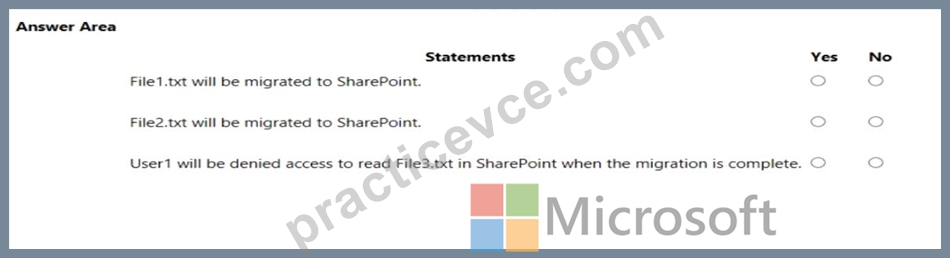
You configure the SharePoint Migration Tool as shown in the exhibit. (Click the Exhibit tab.) For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.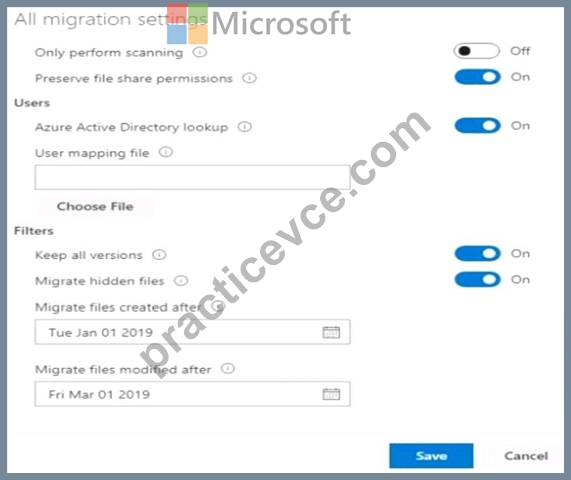
Answer:
Explanation: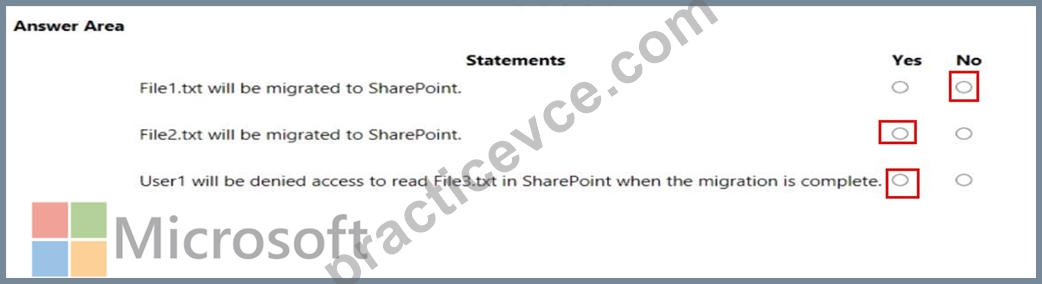
Reference:
https://docs.microsoft.com/en-us/sharepointmigration/spmt-settings
NEW QUESTION # 151
You have a Microsoft 365 subscription and a Microsoft Azure Active Directory (Azure AD) tenant named
contoso.com. Contoso.com contains the users shown in the following table.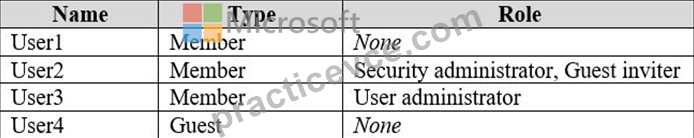
Contoso.com is configured as shown in the following exhibit.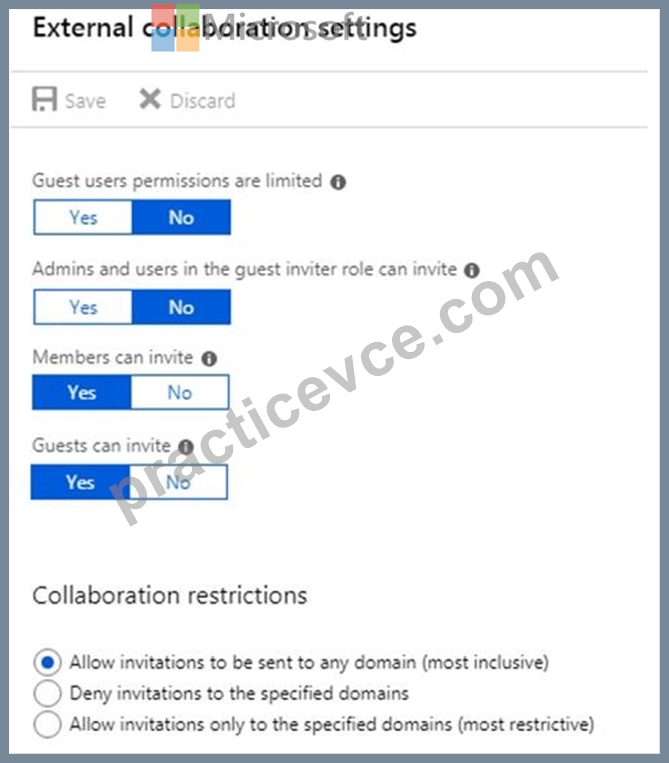
You need to ensure that guest users can be created in the tenant.
Which setting should you modify?
- A. Guests can invite.
- B. Members can invite.
- C. Guests users permissions are limited.
- D. Admins and users in the guest inviter role can invite.
- E. Deny invitations to the specified domains.
Answer: D
Explanation:
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/azure/active-directory/b2b/delegate-invitations
https://docs.microsoft.com/en-us/azure/active-directory/fundamentals/users-default-permissions
NEW QUESTION # 152
Your company has a Microsoft 365 tenant.
You suspect that several Office 365 features were recently updated.
You need to view a list of the features that were recently updated in the tenant.
Solution: You use Reports from the Microsoft Purview compliance portal.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION # 153
You have a Microsoft 365 subscription that contains a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
In the tenant, you create a user named User1.
You need to ensure that User1 can publish retention labels from the Security & Compliance admin center. The solution must use the principle of least privilege.
To which role group should you add User1?
- A. Records Management
- B. Security Administrator
- C. eDiscovery Manager
- D. Compliance Administrator
Answer: D
Explanation:
Explanation
Members of your compliance team who will create retention labels need permissions to the Security & Compliance Center. By default, your tenant admin has access to this location and can give compliance officers and other people access to the Security & Compliance Center, without giving them all of the permissions of a tenant admin. To do this, we recommend that you go to the Permissions page of the Security & Compliance Center, edit the Compliance Administrator role group, and add members to that role group.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/labels#permissions
NEW QUESTION # 154
You need to meet the security requirements for User3. The solution must meet the technical requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.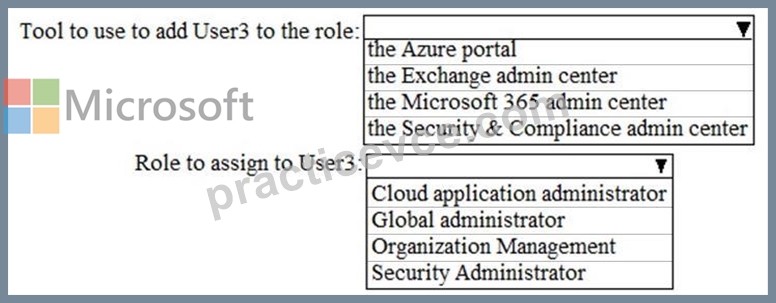
Answer:
Explanation: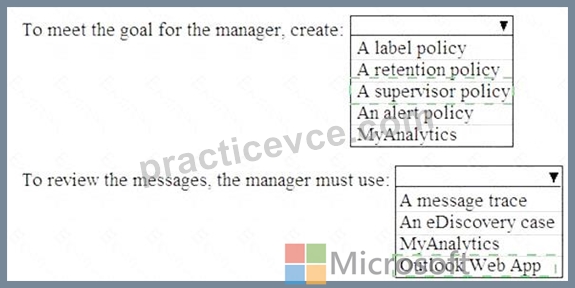
Explanation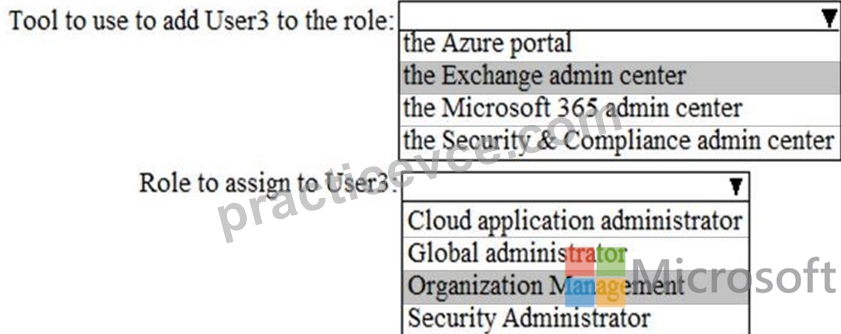
* User3 must be able to manage Office 365 connectors.
* The principle of least privilege must be used whenever possible.
Office 365 connectors are configured in the Exchange Admin Center.
You need to assign User3 the Organization Management role to enable User3 to manage Office 365 connectors.
A Global Admin could manage Office 365 connectors but the Organization Management role has less privilege.
Reference:
https://docs.microsoft.com/en-us/office365/SecurityCompliance/eop/feature-permissions-in-eop
Topic 2, Fabrikam, Inc
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answer and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. When you are ready to answer a question, click the Overview Fabrikam, Inc. is an electronics company that produces consumer products. Fabrikam has 10,000 employees worldwide.
Fabrikam has a main office in London and branch offices in major cities in Europe, Asia, and the United States.
Existing Environment
Active Directory Environment
The network contains an Active Directory forest named fabrikam.com. The forest contains all the identities used for user and computer authentication.
Each department is represented by a top-level organizational unit (OU) that contains several child OUs for user accounts and computer accounts.
All users authenticate to on-premises applications by signing in to their device by using a UPN format of [email protected].
Fabrikam does NOT plan to implement identity federation.
Network Infrastructure
Each office has a high-speed connection to the Internet.
Each office contains two domain controllers. All domain controllers are configured as a DNS server.
The public zone for fabrikam.com is managed by an external DNS server.
All users connect to an on-premises Microsoft Exchange Server 2016 organization. The users access their email by using Outlook Anywhere, Outlook on the web, or the Microsoft Outlook app for iOS. All the Exchange servers have the latest cumulative updates installed.
All shared company documents are stored on a Microsoft SharePoint Server farm.
Requirements
Planned Changes
Fabrikam plans to implement a Microsoft 365 Enterprise subscription and move all email and shared documents to the subscription.
Fabrikam plans to implement two pilot projects:
* Project1: During Project1, the mailboxes of 100 users in the sales department will be moved to Microsoft 365.
* Project2: After the successful completion of Project1, Microsoft Teams & Skype for Business will be enabled in Microsoft 365 for the sales department users.
Fabrikam plans to create a group named UserLicenses that will manage the allocation of all Microsoft 365 bulk licenses.
Technical Requirements
Fabrikam identifies the following technical requirements:
* All users must be able to exchange email messages successfully during Project1 by using their current email address.
* Users must be able to authenticate to cloud services if Active Directory becomes unavailable.
* A user named User1 must be able to view all DLP reports from the Microsoft 365 admin center.
* Microsoft Office 365 ProPlus applications must be installed from a network share only.
* Disruptions to email address must be minimized.
Application Requirements
Fabrikam identifies the following application requirements:
* An on-premises web application named App1 must allow users to complete their expense reports online.
* The installation of feature updates for Office 365 ProPlus must be minimized.
Security Requirements
Fabrikam identifies the following security requirements:
* After the planned migration to Microsoft 365, all users must continue to authenticate to their mailbox and to SharePoint sites by using their UPN.
* The memberships of UserLicenses must be validated monthly. Unused user accounts must be removed from the group automatically.
* After the planned migration to Microsoft 365, all users must be signed in to on-premises and cloud-based applications automatically.
* The principle of least privilege must be used.
NEW QUESTION # 155
Your on-premises network contains the web applications shown in the following table.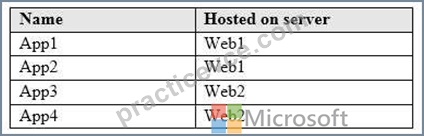
You purchase Microsoft 365, and then implement directory synchronization.
You plan to publish the web applications.
You need to ensure that all the applications are accessible by using the My Apps portal. The solution must minimize administrative effort.
What should you do first?
- A. Create four application registrations.
- B. Deploy one Application Proxy connector.
- C. Deploy one conditional access policy.
- D. Create a site-to-site VPN from Microsoft Azure to the on-premises network.
Answer: B
Explanation:
Section: [none]
Explanation:
The Application Proxy connector is what connects the on-premises environment to the Azure Application Proxy.
Application Proxy is a feature of Azure AD that enables users to access on-premises web applications from a remote client. Application Proxy includes both the Application Proxy service which runs in the cloud, and the Application Proxy connector which runs on an on-premises server. Azure AD, the Application Proxy service, and the Application Proxy connector work together to securely pass the user sign-on token from Azure AD to the web application.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/manage-apps/application-proxy
https://docs.microsoft.com/en-us/azure/active-directory/manage-apps/application-proxy-connectors
NEW QUESTION # 156
You have a Microsoft 365 subscription.
Your company purchases a new financial application named App1.
From Cloud Discovery in Microsoft Cloud App Security, you view the Discovered apps page and discover that many applications have a low score because they are missing information about domain registration and consumer popularity.
You need to prevent the missing information from affecting the score.
What should you configure from the Cloud Discover settings?
- A. App tags
- B. Organization details
- C. Score metrics
- D. Default behavior
Answer: A
Explanation:
References:
https://docs.microsoft.com/en-us/cloud-app-security/discovered-app-queries
NEW QUESTION # 157
Your company has a Microsoft 365 subscription.
You need to identify which users performed the following privileged administration tasks:
* Deleted a folder from the second-stage Recycle Bin if Microsoft SharePoint
* Opened a mailbox of which the user was not the owner
* Reset a user password
What should you use?
- A. Microsoft Azure Active Directory (Azure AD) sign-ins
- B. Security & Compliance audit log search
- C. Microsoft Azure Active Directory (Azure AD) audit logs
- D. Security & Compliance content search
Answer: C
Explanation:
References:
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/activity-logs-overview
NEW QUESTION # 158
Your company is based in the United Kingdom (UK).
Users frequently handle data that contains Personally Identifiable Information (PII).
You create a data loss prevention (DLP) policy that applies to users inside and outside the company. The policy is configured as shown in the following exhibit.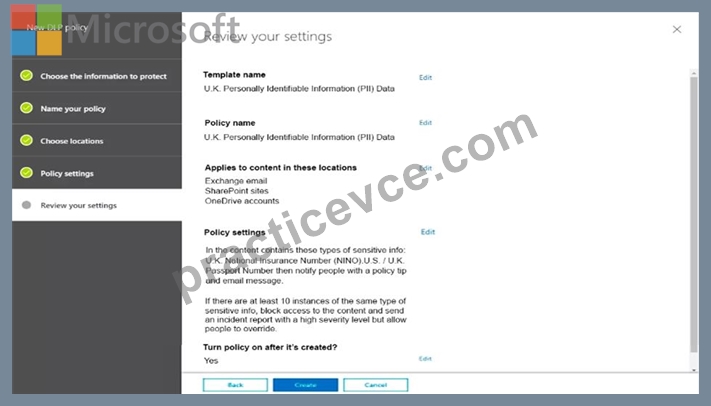
Use the drop-down menus to select the answer choice that completes each statement based in the information presented in the information presented in the graphic.
NOTE: Each correct selection is worth one point.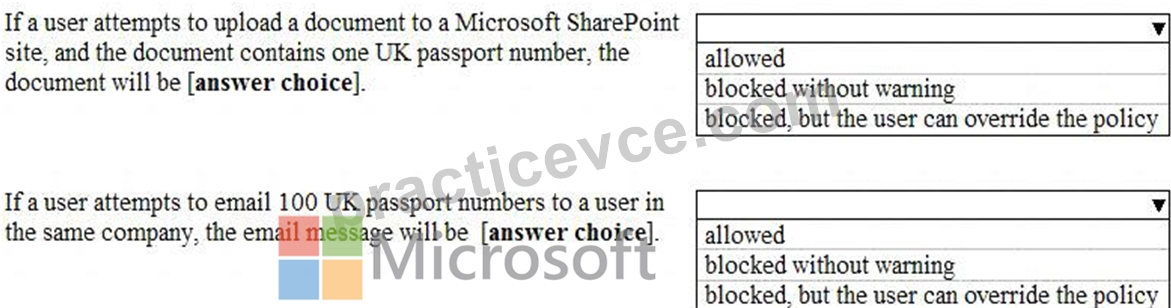
Answer:
Explanation: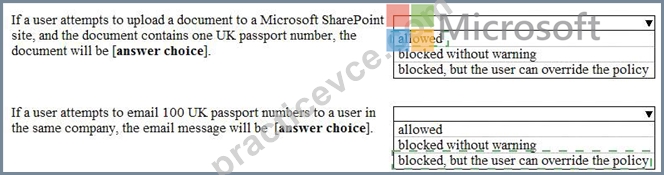
Explanation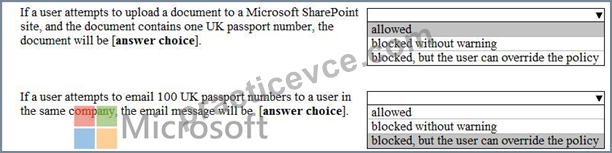
The text in the Policy Settings section of the exhibit explains what will happen.
If a user sends between 1 and 10 instances of the sensitive info (passport number), then a notification email and will be sent to the user and a policy tip will be displayed. The email will not be blocked though. Therefore, it will be allowed.
If a user sends more than 10 instances of the sensitive info (passport number), the email will be blocked and a high-severity alert generated. However, the user can override the block.
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/data-loss-prevention-policies
NEW QUESTION # 159
You have a Microsoft 365 subscription that uses a default named contoso.com.
Three files were created on February 1, 2019, as shown in the following table.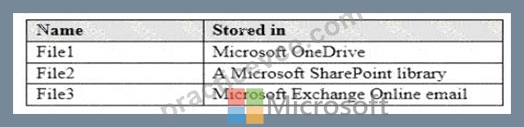
On March 1, 2019, you create two retention labels named Label1 and label2.
The settings for Label1 are configured as shown in the Label1 exhibit. (Click the Label1 tab.) Label 1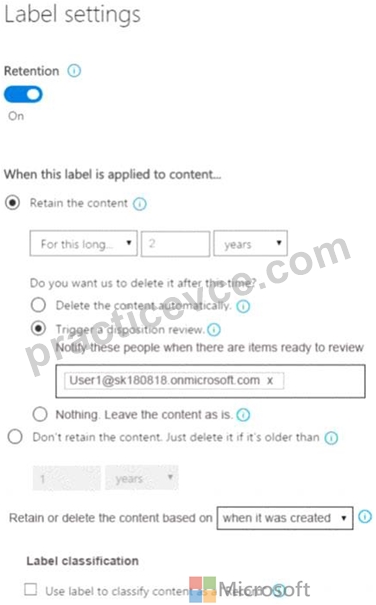
The settings for Label2 are configured as shown in the Label1 exhibit. (Click the Label2 tab.) Label 2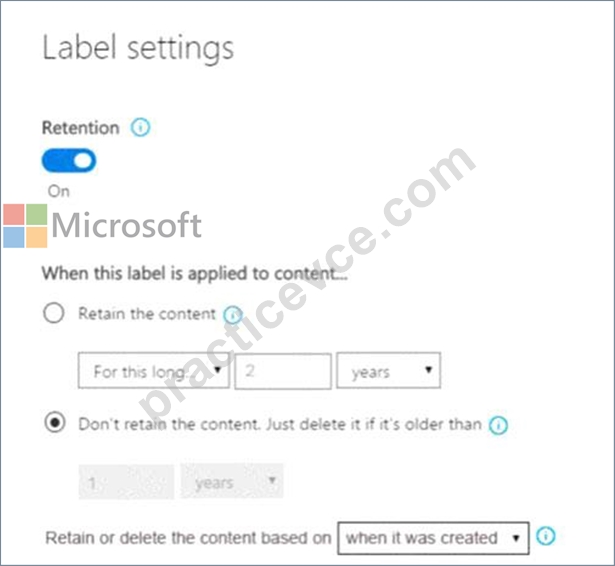
You apply the retention labels to Exchange email, SharePoint sites, and OneDrive accounts.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.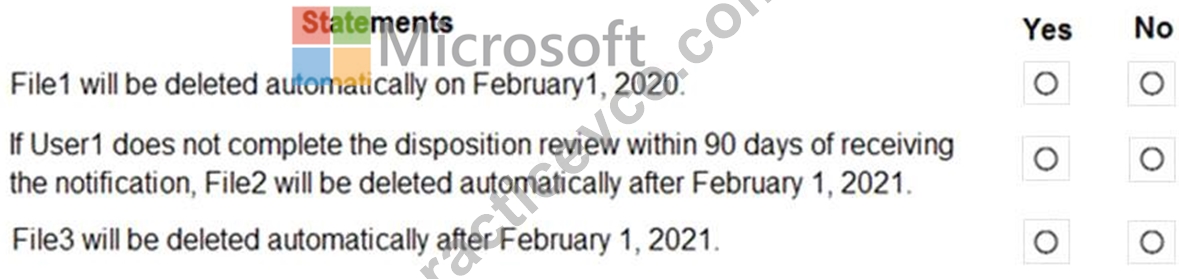
Answer:
Explanation: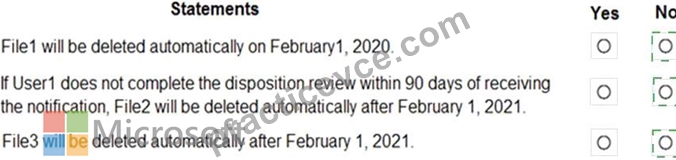
Explanation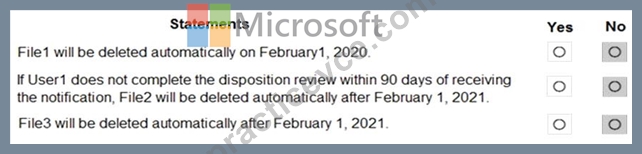
Box 1: No
Retention overrides deletion.
Box 2: No
Content in a document library will be moved to the first-stage Recycle Bin within 7 days of disposition, and then permanently deleted another 93 days after that. Thus 100 days in total.
Box 3: No
Items in an Exchange mailbox will be permanently deleted within 14 days of disposition.
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/labels
https://docs.microsoft.com/en-us/office365/securitycompliance/disposition-reviews
NEW QUESTION # 160
Your network contains an on-premises Active Directory domain named Contoso.com that is synced Azure Active Directory (Azure AD) tenant. The on-premises domain contains a server named ..... 200 client computer that run Windows 10.
Your company purchase a Microsoft 365 subscription.
On server1, you create a file share1. You extract the Microsoft Office Deployment Tool (ODT) to Share1.
You need to deploy Office 365 Proplus and the French languages pack from Share1 to the Windows 10 computers.
Which three actions you perform is sequence? To answer, move the appropriate action from the actions to the answer area and arrange them in the correct order.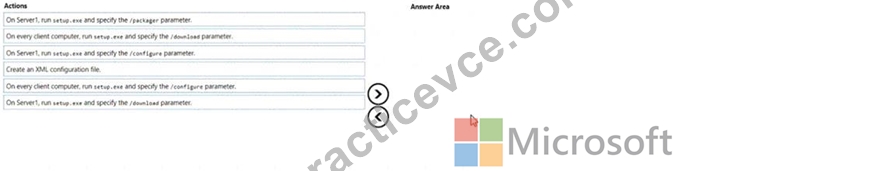
Answer:
Explanation: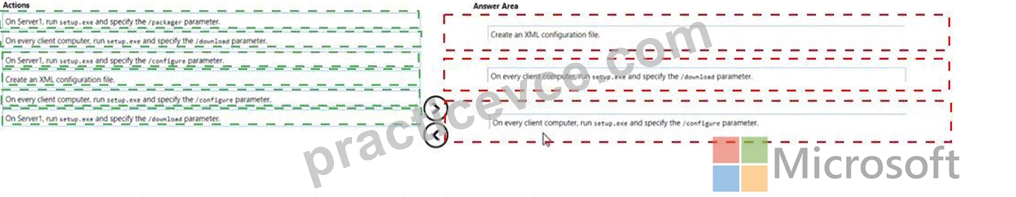
NEW QUESTION # 161
Your network contains an Active Directory forest named contoso.local.
You purchase a Microsoft 365 subscription.
You plan to move to Microsoft and to implement a hybrid deployment solution for the next 12 months.
You need to prepare for the planned move to Microsoft 365.
What is the best action to perform before you implement directory synchronization? More than one answer choice may achieve the goal. Select the BEST answer.
- A. Create an external forest trust.
- B. Purchase a custom domain name.
- C. Rename the Active Directory forest.
- D. Purchase a third-party X.509 certificate.
Answer: C
Explanation:
The first thing you need to do before you implement directory synchronization is to purchase a custom domain name. This could be the domain name that you use in your on-premise Active Directory if it's a routable domain name, for example, contoso.com.
If you use a non-routable domain name in your Active Directory, for example contoso.local, you'll need to add the routable domain name as a UPN suffix in Active Directory.
Reference:
https://docs.microsoft.com/en-us/office365/enterprise/set-up-directory-synchronization
NEW QUESTION # 162
You have retention policies in Microsoft 365 as shown in the following table.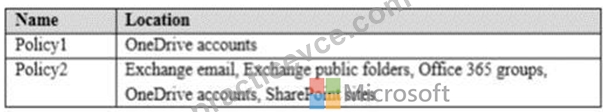
Policy1 is configured as shown in the Policy1 exhibit. (Click the Policy1 tab.) Policy1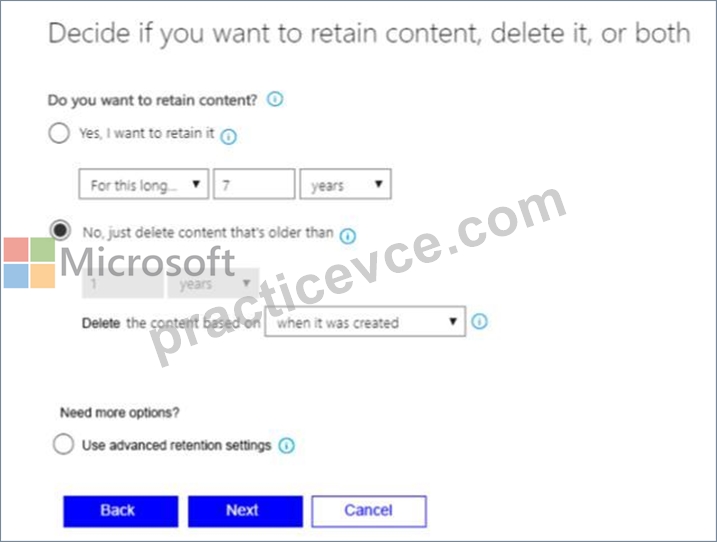
Policy1 is configured as shown in the Policy2 exhibit. (Click the
Policy2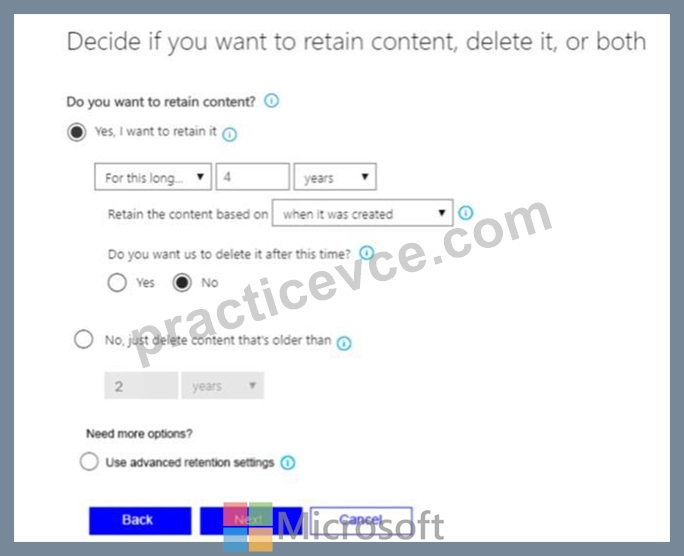
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.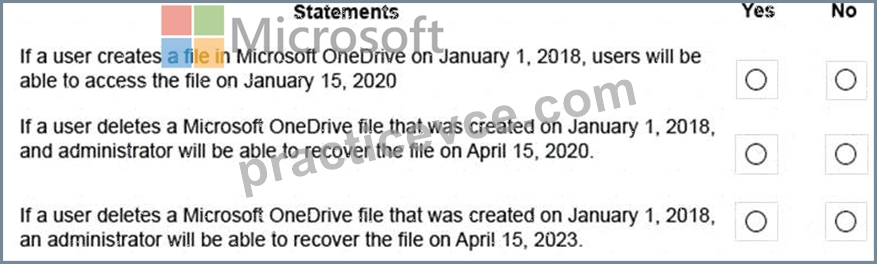
Answer:
Explanation: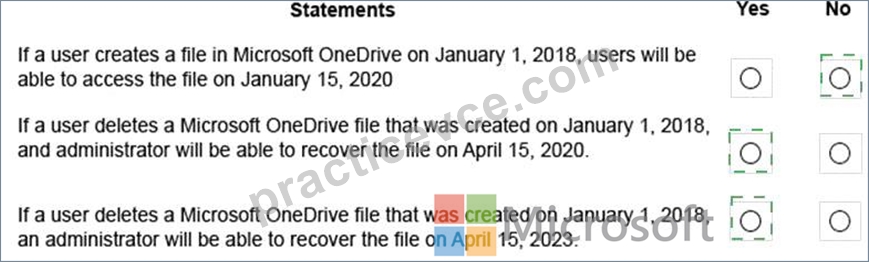
Explanation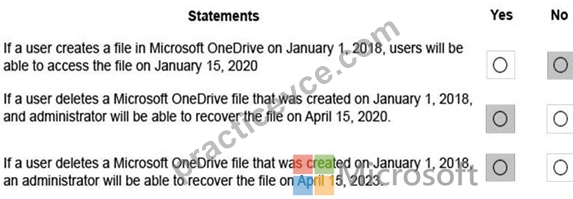
* Retention wins over deletion. Suppose that one retention policy says to delete Exchange email after three years, but another retention policy says to retain Exchange email for five years and then delete it.
Any content that reaches three years old will be deleted and hidden from the users' view, but still retained in the Recoverable Items folder until the content reaches five years old, when it is permanently deleted.
* The longest retention period wins. If content is subject to multiple policies that retain content, it will be retained until the end of the longest retention period.
Box 1: No.
The file will be deleted and hidden from the users' view, but still retained in the Recoverable Items folder. An administrator would need to recover the file.
Box 2: Yes.
The file will be deleted and hidden from the users' view, but still retained in the Recoverable Items folder. An administrator will be able to recover the file.
Box 3: Yes.
2018 to 2023 is five years. Policy2 has a retention period of four years. However, Policy2 is configured to not delete the files after the four-year retention period.
Reference:
https://docs.microsoft.com/en-us/office365/securitycompliance/retention-policies#the-principles-of-retention-or-
NEW QUESTION # 163
Your company uses email, calendar, contact, and task services in Microsoft Outlook.com.
You purchase a Microsoft 365 subscription and plan to migrate all users from Outlook.com to Microsoft 365.
You need to identify which user data can be migrated to Microsoft 365.
Which type of data should you identify?
- A. task
- B. contacts
- C. email
- D. calendar
Answer: C
Explanation:
You can use the Internet Message Access Protocol (IMAP) to migrate user email from Gmail, Exchange, Outlook.com, and other email systems that support IMAP migration. When you migrate the user's email by using IMAP migration, only the items in the users' inbox or other mail folders are migrated. Contacts, calendar items, and tasks can't be migrated with IMAP, but they can be by a user.
Reference:
https://docs.microsoft.com/en-us/exchange/mailbox-migration/mailbox-migration#migrate-email-from-anotherimap-enabled-email-system
NEW QUESTION # 164
......
Updated May-2024 Pass MS-100 Exam - Real Practice Test Questions: https://www.practicevce.com/Microsoft/MS-100-practice-exam-dumps.html
Pass Your Exam With 100% Verified MS-100 Exam Questions: https://drive.google.com/open?id=1e_-nhL99wNodgf6MQKMzmQnI_lPqrdqI